F23: Debug SetVersion root command injection (V3.5.2.1)
original finding or lead
Last updated November 8, 2026
Document type: local CVE candidate assessment, not a published CVE Record. CVE ID: unassigned. Product scope: Anpviz IPC-D240W-S V3.5.2.1 captured from the owner’s MCA40E camera; the V3.6.3.1 comparison image is an MCA50E image sent in error and was not flashed to this model.
Finding
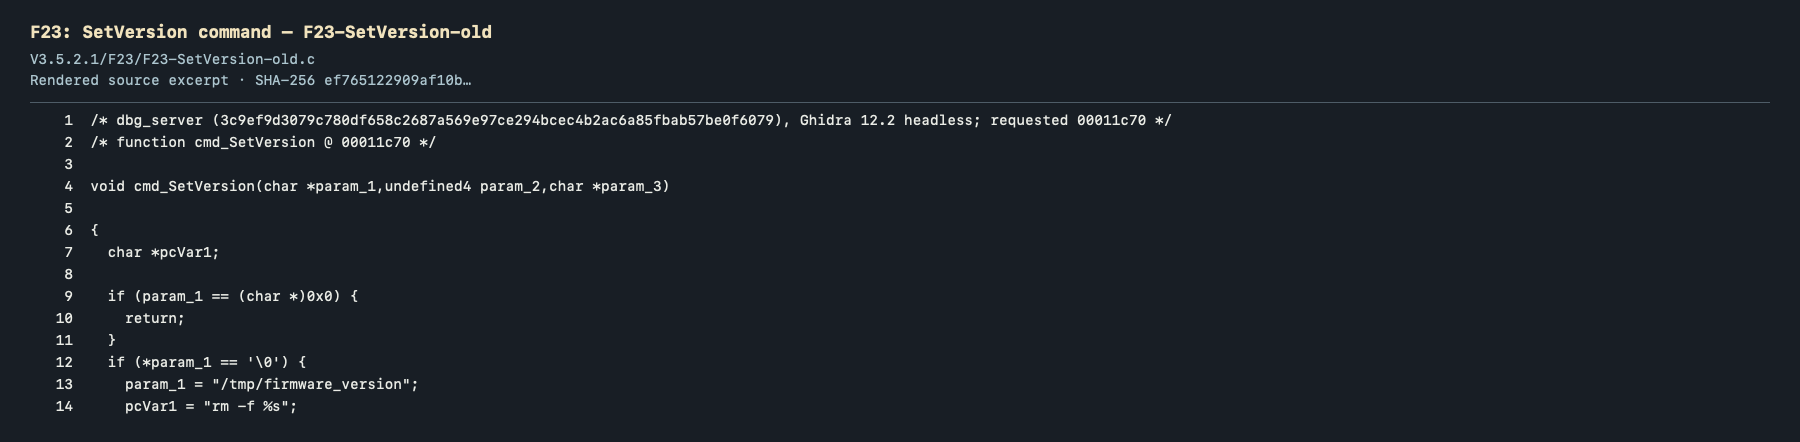
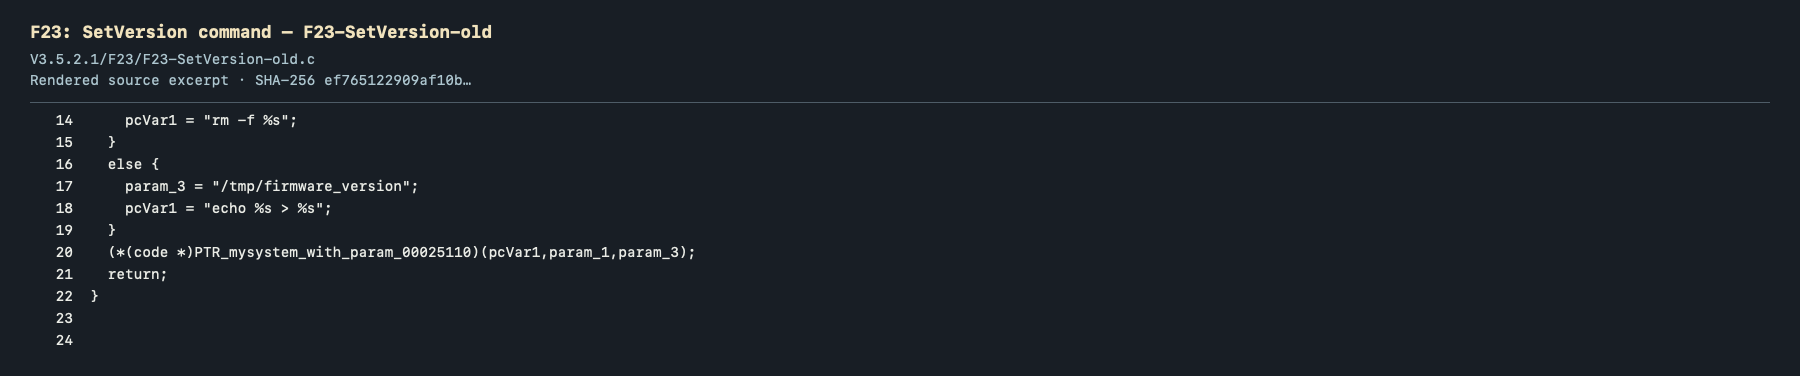
The old debug command placed an argument in a root shell command and was used in a live root-shell test after debug enablement. The new handler validates and writes directly to a file.
Status in this image: original finding or lead.
Evidence limit: Requires the debug service to be enabled with a valid administrator credential in the observed old chain.
Classification and severity
- Proposed CWE: CWE-78
- CVSS v4.0 score: 8.5 High, provisional scenario
- CVSS v4.0 vector:
CVSS:4.0/AV:A/AC:L/AT:N/PR:H/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N - Scoring basis: Old-image scenario includes the administrator credential required to enable debug; new debug-chain behavior was not tested.
- CVE candidacy: Needs coordinator/CNA review for grouping, affected models and version status; do not equate this finding ID with a CVE ID.
Source screenshots
The PNGs are rendered, line-numbered excerpts of existing Ghidra C-like decompilation, not photographs of the Ghidra GUI or recovered vendor source. The original export is authoritative; image selection can omit relevant lines elsewhere in the function.
- F23: SetVersion command — F23-SetVersion-old —
V3.5.2.1/F23/F23-SetVersion-old.clines 1–14; source SHA-256ef765122909af10bba5c040d47ee4af67517d1c4bdf26efe22eb38537e36b91d. - F23: SetVersion command — F23-SetVersion-old —
V3.5.2.1/F23/F23-SetVersion-old.clines 14–24; source SHA-256ef765122909af10bba5c040d47ee4af67517d1c4bdf26efe22eb38537e36b91d.
Related published CVEs
- No verified related CVE linked to this specific finding; this is not an exhaustive database search.
Case references
- Evidence index
- Initial public report
- Remediation review
- CERT/CC VRF #26-10-FZTVG; CISA Case #116607.