F22: Production debug and Telnet capability (V3.5.2.1)
original finding or lead
Last updated November 8, 2026
Document type: local CVE candidate assessment, not a published CVE Record. CVE ID: unassigned. Product scope: Anpviz IPC-D240W-S V3.5.2.1 captured from the owner’s MCA40E camera; the V3.6.3.1 comparison image is an MCA50E image sent in error and was not flashed to this model.
Finding
A valid administrator action enabled a debug service and Telnet in the old image. The new listener adds hash-based login and timeouts but retains the enable and Telnet paths.
Status in this image: original finding or lead.
Evidence limit: Old root shell was observed through the related F23 sink after administrator enablement. New end-to-end behavior is untested.
Classification and severity
- Proposed CWE: CWE-489
- CVSS v4.0 score: 8.5 High, provisional scenario
- CVSS v4.0 vector:
CVSS:4.0/AV:A/AC:L/AT:N/PR:H/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N - Scoring basis: Old-image scenario includes the administrator credential required to enable debug; new debug-chain behavior was not tested.
- CVE candidacy: Needs coordinator/CNA review for grouping, affected models and version status; do not equate this finding ID with a CVE ID.
Source screenshots
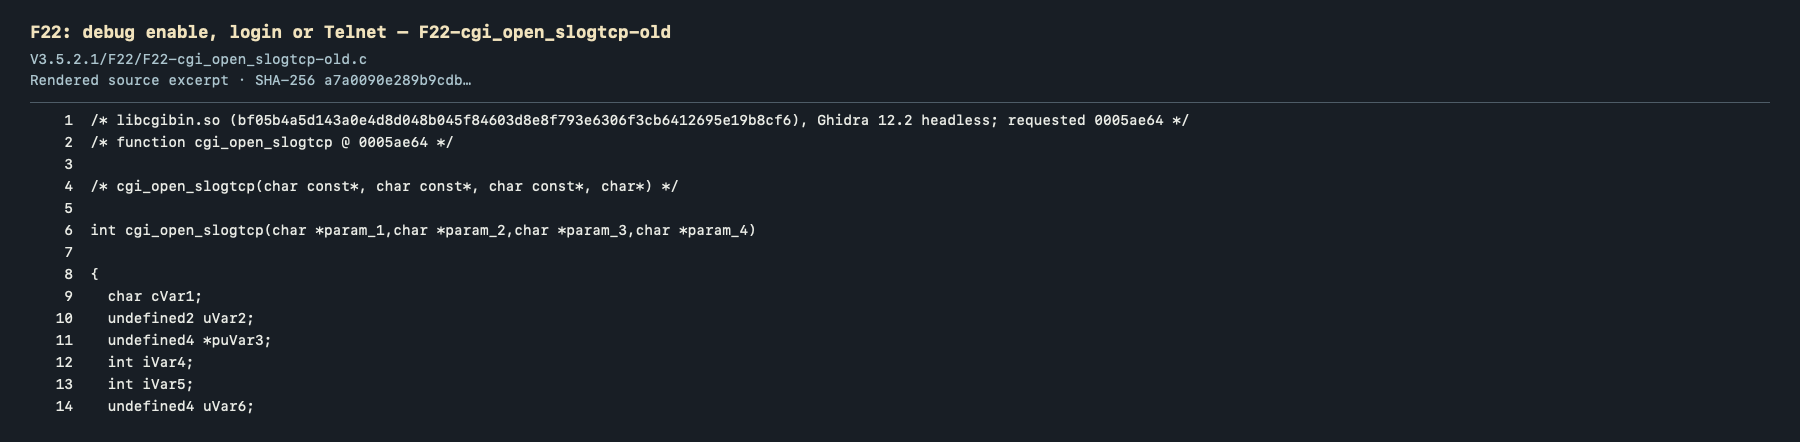
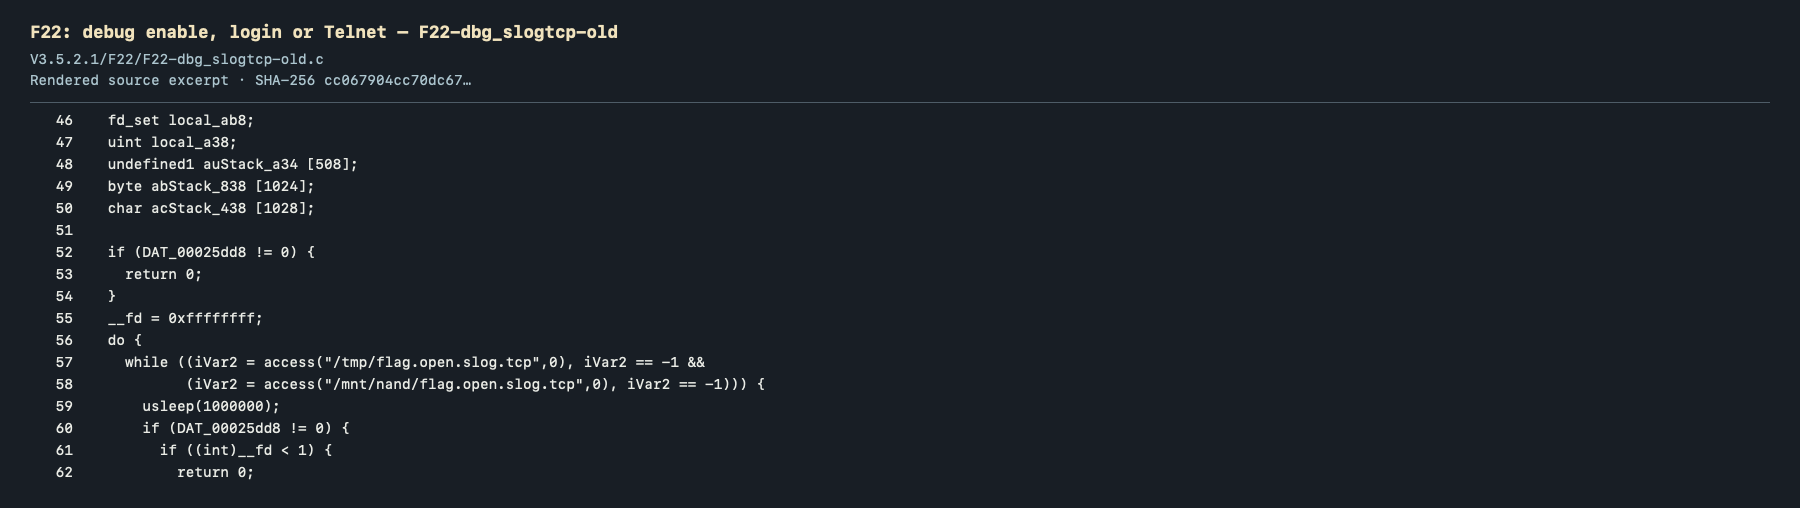
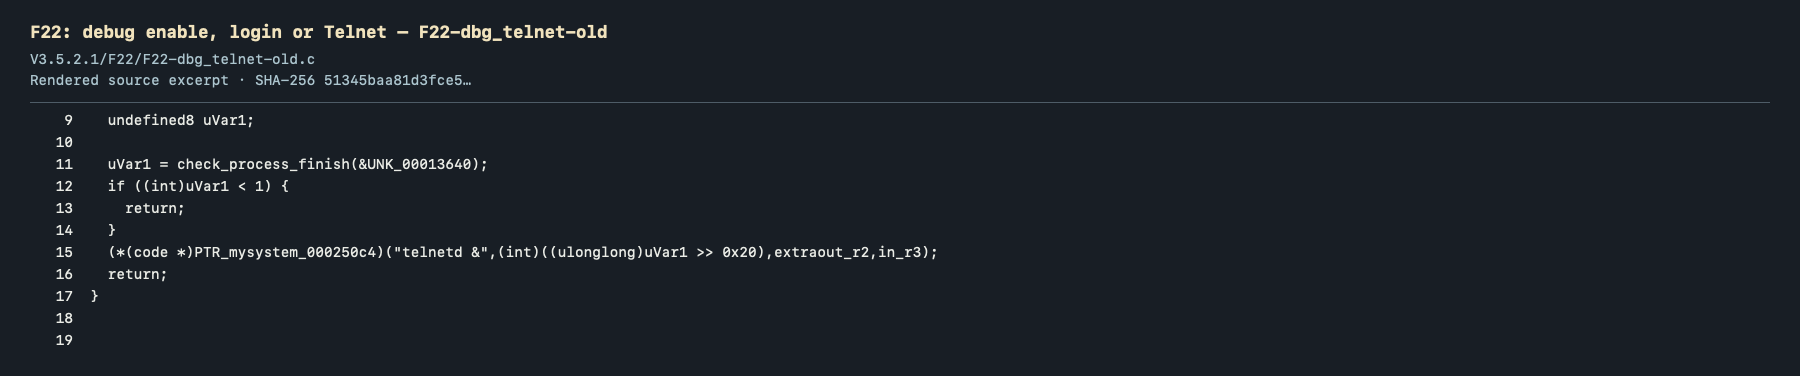
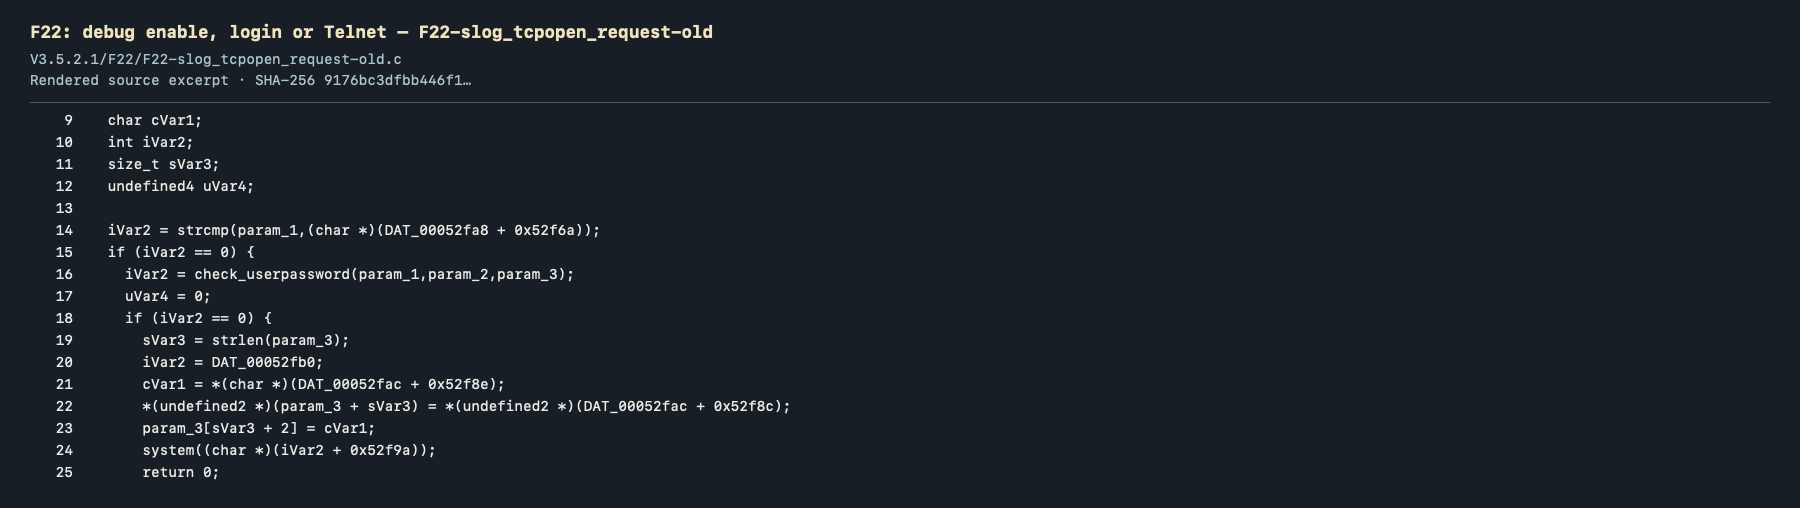
The PNGs are rendered, line-numbered excerpts of existing Ghidra C-like decompilation, not photographs of the Ghidra GUI or recovered vendor source. The original export is authoritative; image selection can omit relevant lines elsewhere in the function.
- F22: debug enable, login or Telnet — F22-cgi_open_slogtcp-old —
V3.5.2.1/F22/F22-cgi_open_slogtcp-old.clines 1–14; source SHA-256a7a0090e289b9cdb734e50081e5c6dcbb5304924c71f4dd99dbeac3f88a224d7. - F22: debug enable, login or Telnet — F22-dbg_slogtcp-old —
V3.5.2.1/F22/F22-dbg_slogtcp-old.clines 46–62; source SHA-256cc067904cc70dc677f63420b16e4f7b68dd2da8696b597b47270d18590f68ba2. - F22: debug enable, login or Telnet — F22-dbg_telnet-old —
V3.5.2.1/F22/F22-dbg_telnet-old.clines 9–19; source SHA-25651345baa81d3fce50f323ced00a22f319bb2e5682cfb6641b1507e4cd7be76cd. - F22: debug enable, login or Telnet — F22-slog_tcpopen_request-old —
V3.5.2.1/F22/F22-slog_tcpopen_request-old.clines 9–25; source SHA-2569176bc3dfbb446f1c430ca4e2354bfa4fd51d6cf8bdd027f0d0dcb8e31238f97.
Related published CVEs
- CVE-2026-100295 — Anjvision YSSD-RTMP-H5 debug interface; different product and issue record. This is not an ID for the IPC-D240W-S case.
Case references
- Evidence index
- Initial public report
- Remediation review
- CERT/CC VRF #26-10-FZTVG; CISA Case #116607.